PET INSURANCE BLOG

AI Cybersecurity Tools: Compare Workflows

Jeffrey Hanschmann

Jeffrey Hanschmann

Licensed Insurance Producer, PIPA Broker
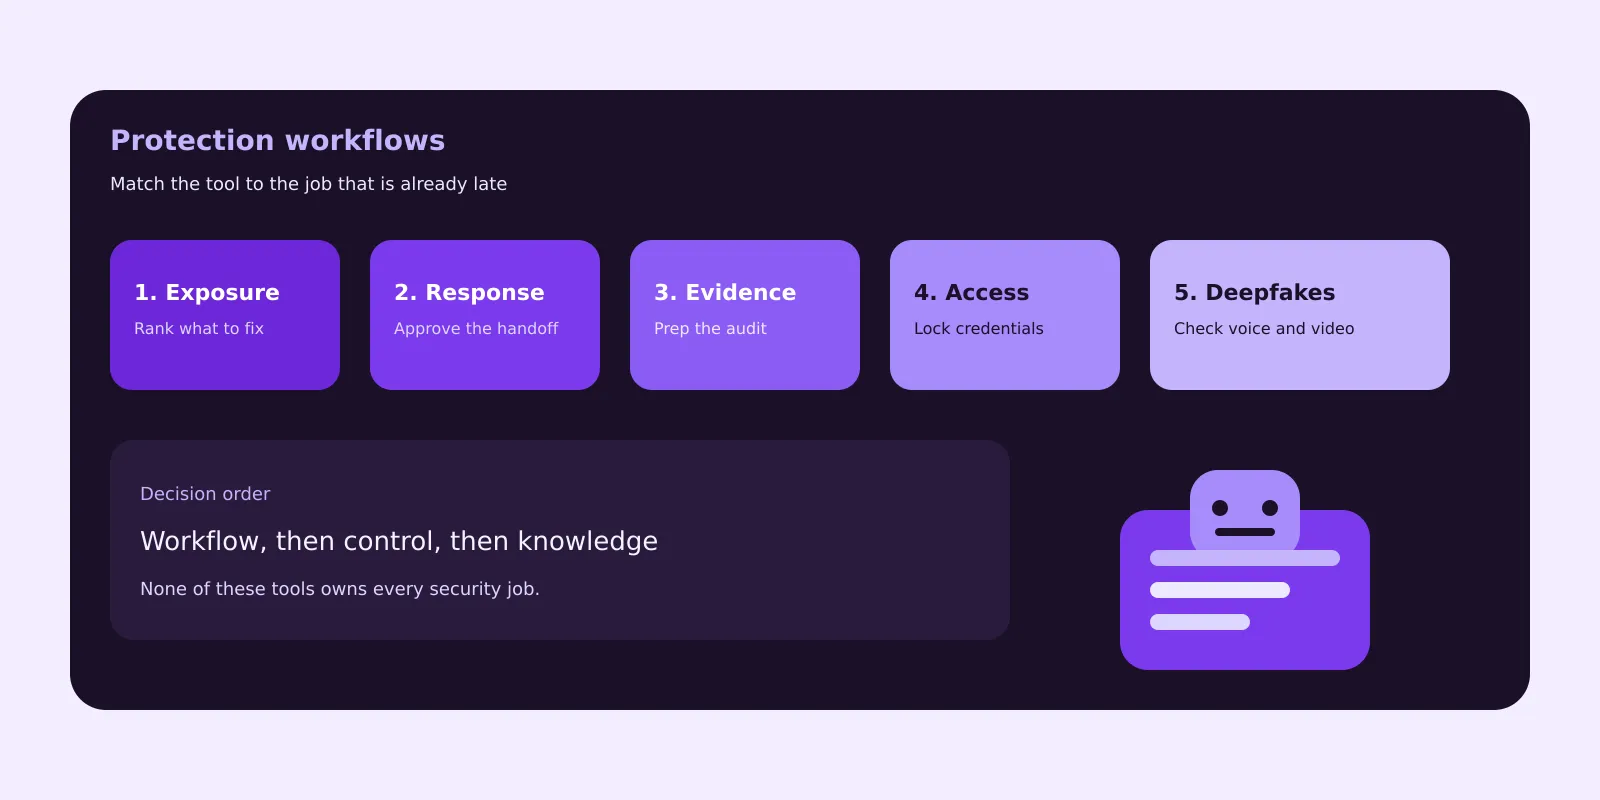
Five labeled protection workflow cards for exposure, response, evidence, access, and deepfakes, with the decision order workflow, control, then knowledge
<p>AI cybersecurity tools do not share one job. Some rank exposures so a team knows what to fix first. Others automate alert handoffs, collect audit evidence, lock down credentials, or check whether a voice or video is synthetic. Compare them by the workflow, the control the team keeps, and how much security knowledge the setup assumes.</p><p data-mega-cta="primary"><a href="tel:+18153557622">Call myAImatch at (815) 355-7622</a> if you want help matching a protection workflow before you add another security subscription.</p><p>NIST's AI Risk Management Framework is a voluntary guide for designing, using, and evaluating AI so risks to people and organizations stay visible (<a href="https://www.nist.gov/itl/ai-risk-management-framework" rel="nofollow" target="_blank">NIST AI RMF</a>). It is not a certification these products hold. Use it as the review frame, then pick the tool that owns the queue that is already late. Each product below is in the <a href="https://www.myaimatch.ai/vault">myAImatch Vault</a> because it fits one protection job, not every control a company needs. <a href="https://www.myaimatch.ai/tools/n8n">n8n</a> is the general workflow builder on the same site. Use it when you are connecting apps you already pay for, not when the job is exposure, audit evidence, or deepfake detection.</p><h2>Compare AI cybersecurity tools by the job they own</h2><p>Start with the bottleneck, not a category label. A team drowning in vulnerability findings needs prioritization. A team that already has findings but spends the day copying alerts between tools needs governed automation. A team preparing for ISO 27001, SOC 2, NIS2, or DORA needs evidence and a person who can sit with the auditor. A team losing track of passwords, passkeys, and SaaS apps needs access control. A team worried about cloned voices and fake media needs detection, not a scanner.</p><table><thead><tr><th>Tool</th><th>Protection workflow</th><th>Control you keep</th><th>Knowledge it assumes</th><th>Starting point on the Vault</th></tr></thead><tbody><tr><td><a href="https://www.myaimatch.ai/tools/tenable">Tenable</a></td><td>Find and rank exposure across vulnerability, cloud, identity, and OT.</td><td>You decide what gets remediated. Hexa AI prioritizes.</td><td>Intermediate. Built for teams that already scan and need a single risk view.</td><td>The Vault lists a free trial and says to request a demo. No public seat price was available.</td></tr><tr><td><a href="https://www.myaimatch.ai/tools/tines">Tines</a></td><td>Automate alert triage, vulnerability handoff, and IT cases with an audit trail.</td><td>Visual Storyboard plus Workbench. You approve what goes live. Cloud or on-premise.</td><td>Intermediate. Security and IT teams who can describe a workflow.</td><td>Free edition on Tines' pricing page, checked 16 Nov 2026: unlimited users and 3 live workflows. Paid editions are custom.</td></tr><tr><td><a href="https://www.myaimatch.ai/tools/copla">Copla</a></td><td>Map controls and collect evidence across frameworks, with a fractional CISO.</td><td>Software plus a named CISO who customizes policy and joins auditor calls.</td><td>Intermediate. Aimed at regulated European organizations, not a first password manager.</td><td>The Vault lists per-framework annual plans. Confirm the current offer with Copla before you budget it.</td></tr><tr><td><a href="https://www.myaimatch.ai/tools/1password">1Password</a></td><td>Store passwords, passkeys, and secrets, and see which SaaS apps people use.</td><td>Role-based vaults and policies. People still choose what to save and share.</td><td>Low to intermediate. Individuals through business admins.</td><td>1Password's business pricing page, checked 16 Nov 2026, lists a 14-day trial. Seat prices change, so read that page before you buy.</td></tr><tr><td><a href="https://www.myaimatch.ai/tools/resemble-ai">Resemble AI</a></td><td>Watermark media and detect deepfakes across voice, image, and video.</td><td>Generate, verify, or detect. Cloud or on-premise, with usage billed per second or call.</td><td>Advanced. Best when impersonation or synthetic media is the actual risk.</td><td>Resemble's pricing page, checked 16 Nov 2026, lists Flex at $0 per month, then Team and Business. Usage rates are extra.</td></tr></tbody></table><p>Read the rows as a situation matrix, not a ranking. None of these is the best AI cybersecurity tool for every company. The right row is the one whose workflow matches the work that is already slipping. Vendor prices move. Where a figure is named later, it is dated to the vendor page checked on 16 November 2026, and you should recheck it before you sign.</p><h2>Which tool fits which protection situation</h2><p>Use this matrix before you open a vendor demo. If two rows feel true, start with the one that removes the current bottleneck. Add the second only after the first workflow is in daily use.</p><table><thead><tr><th>If this is the situation</th><th>Start here</th><th>Why this workflow</th><th>Do not start here</th></tr></thead><tbody><tr><td>Scans exist, but nobody agrees what to fix this week.</td><td>Tenable.</td><td>Exposure management and Hexa AI are built to prioritize findings across cloud, identity, OT, and the attack surface.</td><td>A password manager will not rank vulnerabilities.</td></tr><tr><td>Analysts copy alerts into tickets and the queue never shrinks.</td><td>Tines.</td><td>Storyboard, Cases, and an AI gateway automate triage while keeping an audit log and human approval.</td><td>A compliance suite will not run your SOC playbooks.</td></tr><tr><td>An auditor, insurer, or regulator wants evidence across frameworks.</td><td>Copla.</td><td>Controls map once across DORA, NIS2, ISO 27001, SOC 2, PCI DSS, and Cyber Essentials, with a fractional CISO on the calls.</td><td>Deepfake detection does not produce an evidence room.</td></tr><tr><td>Shared logins, passkeys, and unknown SaaS apps are the leak.</td><td>1Password.</td><td>Watchtower, vault sharing, and SaaS discovery cover the credential workflow most small teams can adopt first.</td><td>An exposure platform is more tool than this job needs.</td></tr><tr><td>Cloned executive voices or synthetic media are the threat.</td><td>Resemble AI.</td><td>Detection and watermarking target generative-media risk. The Vault says the vendor claims coverage against 160+ AI models.</td><td>A workflow builder will not inspect a suspicious voice note.</td></tr></tbody></table><p>myAImatch is a discovery service, not a security operations vendor. The <a href="https://www.myaimatch.ai/assessment">free MAI assessment</a> asks how you work and returns a shortlist from the hand-reviewed Vault. It does not replace a penetration test, a SOC, or a legal review of your controls. If the bottleneck is bigger than one tool, the <a href="https://www.myaimatch.ai/ai-strategy-roadmap">AI Strategy Roadmap</a> is a four-session working engagement, listed at $497 on the service page, to put the rollout in order.</p><h2>Tenable: rank exposure before you chase every alert</h2><p><a href="https://www.myaimatch.ai/tools/tenable">Tenable</a> on the Vault is Tenable One. It pulls vulnerability management, cloud security, identity, OT/IoT, and attack surface management into one view. Nessus remains the scanner underneath, and Hexa AI is the prioritization layer so a team spends time on findings that change risk instead of the longest list.</p><p>The control model is analyst-led. The platform proposes what matters. Your team still owns remediation, patching, and the exception process. The Vault lists the knowledge level as intermediate, which fits a company that already has someone who can read a vulnerability report. It is a poor first tool for a founder who only needs shared passwords.</p><p>The Vault does not publish a seat price. Its profile says the vendor pricing pages were unavailable and that a free trial exists, so the honest next step is a demo or that trial. Confirm scope for cloud, OT, and identity before you assume one subscription covers all three. <a href="https://www.tenable.com/products/tenable-one" rel="nofollow" target="_blank">Tenable's product page</a> is the place to check the current platform description.</p><h2>Tines: automate the security workflow without giving up the audit log</h2><p><a href="https://www.myaimatch.ai/tools/tines">Tines</a> is the workflow tool in this set. It is built for security and IT, not general marketing automation. Storyboard is the visual builder, Workbench is the copilot, and Cases covers incident handling. An AI gateway lets the team choose models and keep a log of what ran.</p><p>That control split matters. People who can describe an alert path can build it without writing a full application, and security still decides what is allowed to go live. The Vault lists cloud or on-premise deployment, SSO/SAML, and SOC 2 Type II. Use Tines when the bottleneck is handoffs: alert triage, vulnerability tickets, or IT requests that bounce between inboxes. Do not use it as a replacement for the scanner or the evidence binder.</p><p>On 16 November 2026, <a href="https://www.tines.com/pricing/" rel="nofollow" target="_blank">Tines' pricing page</a> listed a free edition with unlimited users, spaces, and connectors, three live workflows, and a one-time $50 AI allowance. Paid editions with unlimited workflows were custom, and the page said hosting options are discussed with the team. If you only need to connect two everyday apps you already pay for, read <a href="https://www.myaimatch.ai/blog/workflow-automation-setup">how to set up a first workflow</a> before you buy a security automation platform.</p><h2>Copla: collect compliance evidence and keep a CISO in the loop</h2><p><a href="https://www.myaimatch.ai/tools/copla">Copla</a> is compliance automation plus a fractional CISO, aimed at regulated organizations in Europe. The workflow is cross-framework mapping. Do the control work once, then reuse it for DORA, NIS2, ISO 27001, SOC 2, PCI DSS, and Cyber Essentials. Evidence collection and control monitoring run in the platform. AI helps draft policy. A person still prioritizes tasks and joins auditor calls.</p><p>That last part is the control difference. Copla is not a self-serve scanner with a chatbot. The Vault describes dedicated CISO support, an evidence room, vendor risk, incident reporting, vulnerability scanning, awareness training, and pentesting. Knowledge level is intermediate because someone on your side still has to own the program between audits.</p><p>The Vault lists Copla as annual, per-framework plans rather than a monthly seat price, including an onboarding fee. Those figures were not on Copla's public homepage when this article was checked on 16 November 2026, so they are not repeated here. Confirm the current offer on <a href="https://copla.com/" rel="nofollow" target="_blank">Copla</a> before you budget it. If your only gap is a shared login, this is the wrong purchase.</p><h2>1Password: close the credential workflow first</h2><p><a href="https://www.myaimatch.ai/tools/1password">1Password</a> is the access workflow. It stores passwords, passkeys, two-factor codes, and secure notes, then adds Watchtower for breach monitoring and role-based sharing. Business plans add SCIM, SSO unlock, and integrations the Vault names with Okta, Entra ID, OneLogin, and Duo. SaaS Manager is the discovery piece: see which apps the company is actually using.</p><p>Control stays with the admin and the person saving the item. You choose vaults, policies, and who can view a secret. You do not hand the tool a queue of vulnerabilities to close. That makes it the lowest-knowledge start in this comparison, and often the right first control for a founder or a team under twenty people. It will not tell you which cloud misconfiguration to patch.</p><p>Do not copy an old seat price into a budget. On 16 November 2026, <a href="https://1password.com/pricing/business" rel="nofollow" target="_blank">1Password's business pricing page</a> showed Teams Starter Pack and Business as yearly per-user prices, each with a 14-day trial and no credit card required. The Vault profile still showed an older Business figure, so the vendor page wins. Recheck it for the current amount, currency, and minimum seats before you buy.</p><h2>Resemble AI: detect synthetic media instead of scanning servers</h2><p><a href="https://www.myaimatch.ai/tools/resemble-ai">Resemble AI</a> covers a different threat. The Vault splits it into Generate, Verify, and Detect: voice synthesis with watermarking, watermark checks on audio, image, and video, and deepfake detection. The profile says the vendor claims zero-day coverage against 160+ generative models, plus cloud or on-premise deployment. Treat that coverage claim as the vendor's statement, not a test myAImatch ran.</p><p>This is the advanced row. Use it when the workflow is "prove this audio or video is authentic" or "stop an impersonated executive voice," not when the workflow is patch Tuesday. You keep control of whether you generate, watermark, or only detect, and of whether the deployment is cloud or on-premise. Usage is billed per second or per call on top of the plan.</p><p>On 16 November 2026, <a href="https://www.resemble.ai/pricing" rel="nofollow" target="_blank">Resemble AI's pricing page</a> listed Flex at $0 per month with no subscription fee. Team was $280 per month billed annually, or $350 monthly. Business was $800 per month billed annually, or $1,000 monthly. Enterprise, including on-premises deployment, was quote-only. Audio detection on Flex was listed at $0.035 per second. A model score is an input to a review, not a court finding.</p><h2>What to verify before you trust any of these tools</h2><p>IBM's overview of AI in cybersecurity says the value is faster investigation and response, not a second security team (<a href="https://www.ibm.com/solutions/ai-cybersecurity" rel="nofollow" target="_blank">IBM</a>). A listing in the Vault is a reviewed starting point. It is not a penetration test, a SOC 2 inheritance letter, or a promise that the vendor's price and features stay frozen. The standard for how myAImatch reviews a tool, and what a listing does not prove, is in <a href="https://www.myaimatch.ai/blog/how-we-review-every-tool-in-the-vault">how we review every tool in the Vault</a>.</p><ul><li><strong>Workflow fit.</strong> Name the queue that is late this month. Exposure, triage, audit evidence, credentials, or synthetic media. Buy the tool that owns that queue.</li><li><strong>Control.</strong> Decide who can approve a remediation, a live automation, a policy, a shared vault, or a deepfake verdict. If the product hides that decision, it is the wrong level of control.</li><li><strong>Knowledge.</strong> Intermediate tools assume someone can read findings or describe a playbook. Do not staff Tenable or Copla with a signup and no owner.</li><li><strong>Data and deployment.</strong> Ask where prompts, alerts, evidence, and voice samples are stored, and whether on-premise is actually available on the plan you can buy.</li><li><strong>Price shape.</strong> A custom workflow quote, an annual framework plan, a per-user credential plan, and a per-second media rate are not one spreadsheet cell. Compare them only after the workflow is chosen, and only from the vendor page dated the day you check.</li></ul><p>When you put one workflow into practice, use the <a href="https://www.myaimatch.ai/blog/ai-implementation-checklist">AI implementation checklist</a>. Set access, ownership, and a rollback step before the first alert or the first audit export. For a broader shortlist outside security, <a href="https://www.myaimatch.ai/blog/how-to-evaluate-ai-tools-for-a-small-business">how to evaluate AI tools for a small business</a> covers fit, cost, and adoption without mixing in a scanner.</p><p data-mega-cta="secondary"><a href="https://www.myaimatch.ai/assessment">Take the free MAI assessment</a> and get a shortlist matched to the protection workflow that is already late.</p><h2>Frequently asked questions</h2><h3>What are AI cybersecurity tools?</h3><p>They are security products that use machine learning or generative AI to detect, prioritize, document, or respond to risk. In this comparison that means exposure ranking, security workflow automation, compliance evidence, credential protection, and deepfake detection. They do not all belong in one stack on day one.</p><h3>Which AI cybersecurity tool should a small team buy first?</h3><p>If the failure is shared passwords and unknown apps, start with 1Password. If the failure is an audit deadline, start with Copla. If the failure is an unscored vulnerability backlog or an alert queue, start with Tenable or Tines. Match the tool to the late workflow.</p><h3>Does an AI cybersecurity tool replace a security person?</h3><p>No. Tenable still needs someone to remediate. Tines still needs someone to approve what goes live. Copla includes fractional CISO support because software alone does not sit on the auditor call. The tools change the workflow. They do not remove ownership.</p><h3>Are these tools a compliance certification?</h3><p>No. Copla helps you organize evidence for frameworks such as ISO 27001, SOC 2, NIS2, and DORA. Tines lists SOC 2 Type II for its own platform. Neither fact certifies your company. Your auditor, your scope, and your evidence still decide that.</p><h3>How does myAImatch fit in?</h3><p>myAImatch reviews tools by hand and matches them to how you work. The free assessment returns a shortlist from the Vault. It does not operate your SOC. A Visit link on a Vault profile may be a paid referral, and rankings stay based on fit and review. Read each profile, then confirm price and deployment on the vendor's site.</p><h2>Start from the workflow that is already late</h2><p>Pick the protection job first. Then take the short assessment so the next tool matches the work, not a generic "best of" list.</p><ol><li>Rank exposures with Tenable when the backlog has no owner.</li><li>Automate the handoff with Tines when alerts sit in inboxes.</li><li>Build the evidence room with Copla when an audit date is real.</li><li>Lock credentials with 1Password when shared logins are the leak.</li><li>Inspect synthetic media with Resemble AI when a voice or video is the threat.</li></ol><p>If you would rather talk it through, <a href="tel:+18153557622">call myAImatch at (815) 355-7622</a>. The number is the public contact on the customer record.</p>